Breach Notification , Cybercrime , Fraud Management & Cybercrime
Macy's E-Commerce Site Hacked
Payment Card Data Stolen by JavaScript Added to Checkout and 'My Account' Pages
Mathew J. Schwartz (euroinfosec) • November 19, 2019
Macy's E-Commerce Site Hacked
Macy's flagship store in New York (Photo: Macy's)
Department store giant Macy's says hackers successfully infiltrated its e-commerce site and stole customer data, including financial information.
See Also: Webinar | Passwords: Here Today, Gone Tomorrow? Be Careful What You Wish For.
A data breach notification from Macy's, dated Nov. 14, says that the company received an alert about "a suspicious connection between macys.com and another website" on Oct. 15, which led it to immediately launch an investigation.
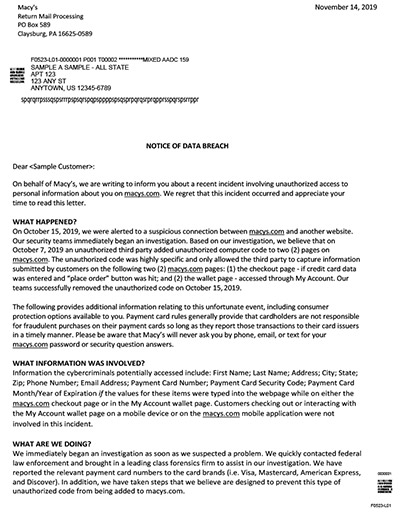
Macy's breach notification, dated Nov. 14, 2019 (Source: Bleeping Computer)
"We quickly contacted federal law enforcement and brought in a leading-class forensics firm to assist in our investigation," says Cincinnati-based Macy's, which reported 2018 sales of $25 billion. The company operates about 680 department stores under the Macy's and Bloomingdale's brands, while also running a further 190 specialty stores under such names as Bloomingdale's The Outlet and Macy's Backstage, across 43 states, as well as Puerto Rico, Guam and Washington.
"Based on our investigation, we believe that on Oct. 7, an unauthorized third party added unauthorized computer code to two pages on macys.com," the notification says. "The unauthorized code was highly specific and only allowed the third party to capture information submitted by customers on the following two macys.com pages: the checkout page - if credit card data was entered and "place order" button was hit; and the wallet page - accessed through My Account."
Card Data at Risk
Stolen data potentially includes the following, if they had been entered by a customer while they were on the "My Wallet" or checkout pages: name, full address, phone number, email address, payment card number, card security code and card month/year of expiration.
Macy's says only users of its website - but not mobile applications - were at risk.
The retailer said it expunged the rogue code on Oct. 15.
Bleeping Computer, which first reported on the breach, says that the code planted on Macy's site appears to have involved malicious JavaScript code connected to Magecart.
Magecart is "an umbrella term given to at least seven cybercriminal groups that are placing digital credit card skimmers on compromised e-commerce sites at an unprecedented rate and with frightening success," security firms RiskIQ and Flashpoint said in a report issued last year. At that time, they warned that these card-skimming attacks had already been used to successfully infiltrate and steal card data from more than 100,000 e-commerce sites.
Since then, attackers wielding webskimmers - aka digital or JavaScript skimmers, or JavaScript sniffers - to steal payment information have continued to hit numerous sites (see Magecart Group Continues Targeting E-Commerce Sites).
Number of Victims Not Disclosed
Reached for comment, officials at Macy's declined to quantify the number of breach victims or stolen payment cards, or whether it could confirm if Magecart scripts had been running on its site. "We are aware of a data security incident involving a small number of our customers on Macys.com," a spokeswoman tells Information Security Media Group. "We have investigated the matter thoroughly, addressed the cause and have implemented additional security measures as a precaution. All impacted customers have been notified, and we are offering consumer protections to these customers at no cost."
Macy's says it has been directly notifying affected customers via email, advising them to watch their financial statements for signs of fraud, which it notes will be reimbursed by card issuers. It's also offering all victims Experian's IdentityWorks identity fraud monitoring services, prepaid for 12 months.
The data breach notification issued by Macy's says the retailer has shared all of the compromised payment card numbers with Visa, MasterCard, American Express and Discover.
Bleeping Computer reports that it was contacted by a security researcher, who wished to remain anonymous, who reported that Macy's attackers compromised the site and altered a script - found at "https://www.macys.com/js/min/common/util/ClientSideErrorLog.js" to include hidden Magecart code.
"The researcher told us that when a customer submitted their payment information, this script would launch and send the submitted information to a command and control server," which attackers could retrieve by logging into the server, Bleeping Computer reports.
The obfuscated Magescript planted by attackers inside Macy's website.
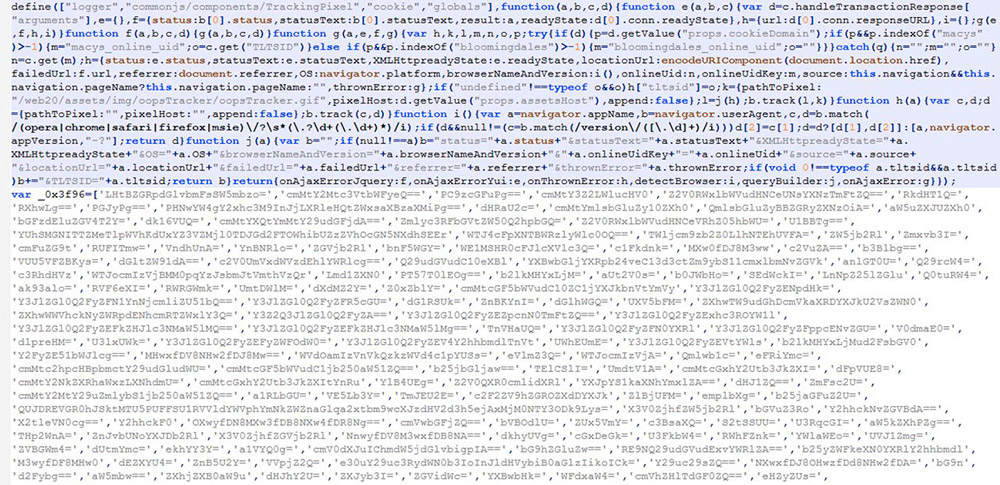
(Source: Bleeping Computer)
Credential-Stuffing Attacks
This isn't the first data breach notification to have been issued by Macy's. In June 2018, for example, Macy's notified customers that it had detected fraudulent attempts to use legitimate usernames and passwords to access customer accounts.
"On June 11, 2018, our cyberthreat alert tools detected suspicious login activities related to certain macys.com customer online profiles using valid usernames and passwords," according to Macy's data breach notification to victims, dated June 27, 2018.
"We immediately began an investigation. Based on our investigation, we believe that an unauthorized third party, from approximately April 26, 2018, through June 12, 2018, used valid customer usernames and passwords to login to customer online profiles. We believe the third party obtained these customer usernames and passwords from a source other than Macy's."
As noted, such credential-stuffing attacks don't involve a breach at the organization where the accounts are being targeted. Rather, attackers use lists of usernames - often email addresses - and passwords stolen from other breaches and try them across a number of sites to see where else victims have reused the same password (see: Credential Stuffing Attacks: How to Combat Reused Passwords).
When attackers were able to reuse username and password pairs to access Macy's accounts, they were able to obtain a wide range of data. "After logging into a macys.com online profile, the unauthorized party was able to access the following information available in the profile: first and last name; full address; phone number; email address; birthday (month & day only) and debit or credit card number with expiration dates," Macy's said in its breach notification. "Macys.com online profiles do not include credit verification values (CVV) or Social Security numbers," it added. "As a result, this information was not accessed."
Macy's said that on June 12, 2018, it had blocked all accounts tied to any suspicious access patterns, until customers changed their passwords.
Macy's E-Commerce Site Hacked
Payment Card Data Stolen by JavaScript Added to Checkout and 'My Account' Pages
Mathew J. Schwartz (euroinfosec) • November 19, 2019
Macy's E-Commerce Site Hacked
Macy's flagship store in New York (Photo: Macy's)
Department store giant Macy's says hackers successfully infiltrated its e-commerce site and stole customer data, including financial information.
See Also: Webinar | Passwords: Here Today, Gone Tomorrow? Be Careful What You Wish For.
A data breach notification from Macy's, dated Nov. 14, says that the company received an alert about "a suspicious connection between macys.com and another website" on Oct. 15, which led it to immediately launch an investigation.
Macy's breach notification, dated Nov. 14, 2019 (Source: Bleeping Computer)
"We quickly contacted federal law enforcement and brought in a leading-class forensics firm to assist in our investigation," says Cincinnati-based Macy's, which reported 2018 sales of $25 billion. The company operates about 680 department stores under the Macy's and Bloomingdale's brands, while also running a further 190 specialty stores under such names as Bloomingdale's The Outlet and Macy's Backstage, across 43 states, as well as Puerto Rico, Guam and Washington.
"Based on our investigation, we believe that on Oct. 7, an unauthorized third party added unauthorized computer code to two pages on macys.com," the notification says. "The unauthorized code was highly specific and only allowed the third party to capture information submitted by customers on the following two macys.com pages: the checkout page - if credit card data was entered and "place order" button was hit; and the wallet page - accessed through My Account."
Card Data at Risk
Stolen data potentially includes the following, if they had been entered by a customer while they were on the "My Wallet" or checkout pages: name, full address, phone number, email address, payment card number, card security code and card month/year of expiration.
Macy's says only users of its website - but not mobile applications - were at risk.
The retailer said it expunged the rogue code on Oct. 15.
Bleeping Computer, which first reported on the breach, says that the code planted on Macy's site appears to have involved malicious JavaScript code connected to Magecart.
Magecart is "an umbrella term given to at least seven cybercriminal groups that are placing digital credit card skimmers on compromised e-commerce sites at an unprecedented rate and with frightening success," security firms RiskIQ and Flashpoint said in a report issued last year. At that time, they warned that these card-skimming attacks had already been used to successfully infiltrate and steal card data from more than 100,000 e-commerce sites.
Since then, attackers wielding webskimmers - aka digital or JavaScript skimmers, or JavaScript sniffers - to steal payment information have continued to hit numerous sites (see Magecart Group Continues Targeting E-Commerce Sites).
Number of Victims Not Disclosed
Reached for comment, officials at Macy's declined to quantify the number of breach victims or stolen payment cards, or whether it could confirm if Magecart scripts had been running on its site. "We are aware of a data security incident involving a small number of our customers on Macys.com," a spokeswoman tells Information Security Media Group. "We have investigated the matter thoroughly, addressed the cause and have implemented additional security measures as a precaution. All impacted customers have been notified, and we are offering consumer protections to these customers at no cost."
Macy's says it has been directly notifying affected customers via email, advising them to watch their financial statements for signs of fraud, which it notes will be reimbursed by card issuers. It's also offering all victims Experian's IdentityWorks identity fraud monitoring services, prepaid for 12 months.
The data breach notification issued by Macy's says the retailer has shared all of the compromised payment card numbers with Visa, MasterCard, American Express and Discover.
Bleeping Computer reports that it was contacted by a security researcher, who wished to remain anonymous, who reported that Macy's attackers compromised the site and altered a script - found at "https://www.macys.com/js/min/common/util/ClientSideErrorLog.js" to include hidden Magecart code.
"The researcher told us that when a customer submitted their payment information, this script would launch and send the submitted information to a command and control server," which attackers could retrieve by logging into the server, Bleeping Computer reports.
The obfuscated Magescript planted by attackers inside Macy's website.
(Source: Bleeping Computer)
Credential-Stuffing Attacks
This isn't the first data breach notification to have been issued by Macy's. In June 2018, for example, Macy's notified customers that it had detected fraudulent attempts to use legitimate usernames and passwords to access customer accounts.
"On June 11, 2018, our cyberthreat alert tools detected suspicious login activities related to certain macys.com customer online profiles using valid usernames and passwords," according to Macy's data breach notification to victims, dated June 27, 2018.
"We immediately began an investigation. Based on our investigation, we believe that an unauthorized third party, from approximately April 26, 2018, through June 12, 2018, used valid customer usernames and passwords to login to customer online profiles. We believe the third party obtained these customer usernames and passwords from a source other than Macy's."
As noted, such credential-stuffing attacks don't involve a breach at the organization where the accounts are being targeted. Rather, attackers use lists of usernames - often email addresses - and passwords stolen from other breaches and try them across a number of sites to see where else victims have reused the same password (see: Credential Stuffing Attacks: How to Combat Reused Passwords).
When attackers were able to reuse username and password pairs to access Macy's accounts, they were able to obtain a wide range of data. "After logging into a macys.com online profile, the unauthorized party was able to access the following information available in the profile: first and last name; full address; phone number; email address; birthday (month & day only) and debit or credit card number with expiration dates," Macy's said in its breach notification. "Macys.com online profiles do not include credit verification values (CVV) or Social Security numbers," it added. "As a result, this information was not accessed."
Macy's said that on June 12, 2018, it had blocked all accounts tied to any suspicious access patterns, until customers changed their passwords.